

21st September 2026
By Shubhii Verma
Chinese open-source AI models are being linked to a sharp increase in malware commands hosted on blockchains, with Chainalysis reporting a 440% rise in malicious on-chain activity since mid-2025.
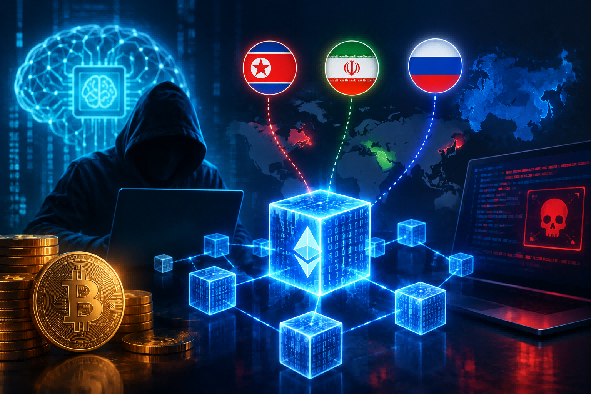
According to the blockchain analytics firm, daily malicious blockchain writes increased from an average of 2.06 to 11.1 in less than a year. Chainalysis refers to the technique as “blockchain dead drops” (BDDs), in which attackers place malware instructions, payloads, or infrastructure details inside blockchain transactions and smart contracts. Compromised devices can then retrieve those instructions on demand.
Why Hackers Are Turning to Blockchain Dead Drops
The attraction is persistence. Traditional command-and-control servers can be seized, blocked, or taken offline, while information recorded on public blockchains can remain accessible indefinitely. Chainalysis said the technique has existed since 2013, when a Necurs botnet variant used Namecoin to store domains. The approach later expanded to Ethereum Virtual Machine-compatible networks through a technique known as EtherHiding.
Chinese AI Models Lower the Barrier for Blockchain Malware
Chainalysis said the recent surge began around mid-2025, coinciding with powerful Chinese open-weight AI models that could generate malicious code without restrictions found in many commercial systems. The firm said this lowered the technical barrier for attackers seeking to build blockchain-based command systems.
State-Linked Hackers Expand Blockchain Malware Activity
The activity is increasingly associated with state-linked groups. Through early 2024, cybercriminals accounted for nearly all observed blockchain dead-drop activity. By the second quarter of 2026, state-linked operators were responsible for roughly two-thirds of new activity each quarter and about half of total activity.
North Korea-linked UNC5342 reportedly operates a three-chain relay involving TRON, Aptos, and BNB Smart Chain. Attackers can publish new transactions to rotate infrastructure, allowing infected devices to automatically receive updated instructions.
Suspected Iranian operators have reportedly used tiny Bitcoin payments to a known address associated with Satoshi Nakamoto, embedding information in transactions that malware can decode to identify current infrastructure.
Russian-language criminal groups have adopted the model commercially, with one Polygon-based operator reportedly managing resolver contracts for multiple customers.
Blockchain Malware Creates a New Challenge for Cybersecurity
The growing use of blockchains creates a difficult challenge for defenders because blocking blockchain traffic could disrupt legitimate applications. However, the public nature of blockchain records gives investigators a permanent trail of malicious updates, potentially providing evidence for tracking operations.